How to Prevent SSRF Vulnerabilities in Backend Services
Learn how to effectively prevent SSRF vulnerabilities in your backend services to ensure robust security.
Introduction
Server-Side Request Forgery (SSRF) is a critical security vulnerability that can lead to unauthorized access to internal services through a vulnerable backend. To prevent SSRF, developers need to implement best practices and security measures at various levels of the application stack.
Key takeaways
- Understand what SSRF vulnerabilities are and how they can be exploited.
- Implement strict input validation to mitigate risk.
- Use network segmentation to protect sensitive services.
- Employ whitelisting for outbound requests to validate intended targets.
- Regularly audit and monitor your applications and services.
What is SSRF?
Server-Side Request Forgery (SSRF) occurs when a server processes a request provided by a client, allowing an attacker to send crafted requests to internal services that are not directly accessible to the public. SSRF can lead to data leakage, unauthorized actions on internal services, and even full server compromise.
How to Prevent SSRF
Preventing SSRF requires a proactive approach at various levels of your backend services. Here are effective strategies:
1. Input Validation
Always validate and sanitize user inputs, especially URLs. Use libraries or frameworks that can help ensure that the input meets a specific format. For example, if you are allowing users to input a URL, only accept URLs from trusted domains or that start with specific schemas (http, https).
function isValidUrl(url) {
  const regex = /^(http|https):\/\/.test(url);
  return regex;
}

if (!isValidUrl(userInput)) {
  throw new Error('Invalid URL');
}
2. Network Segmentation
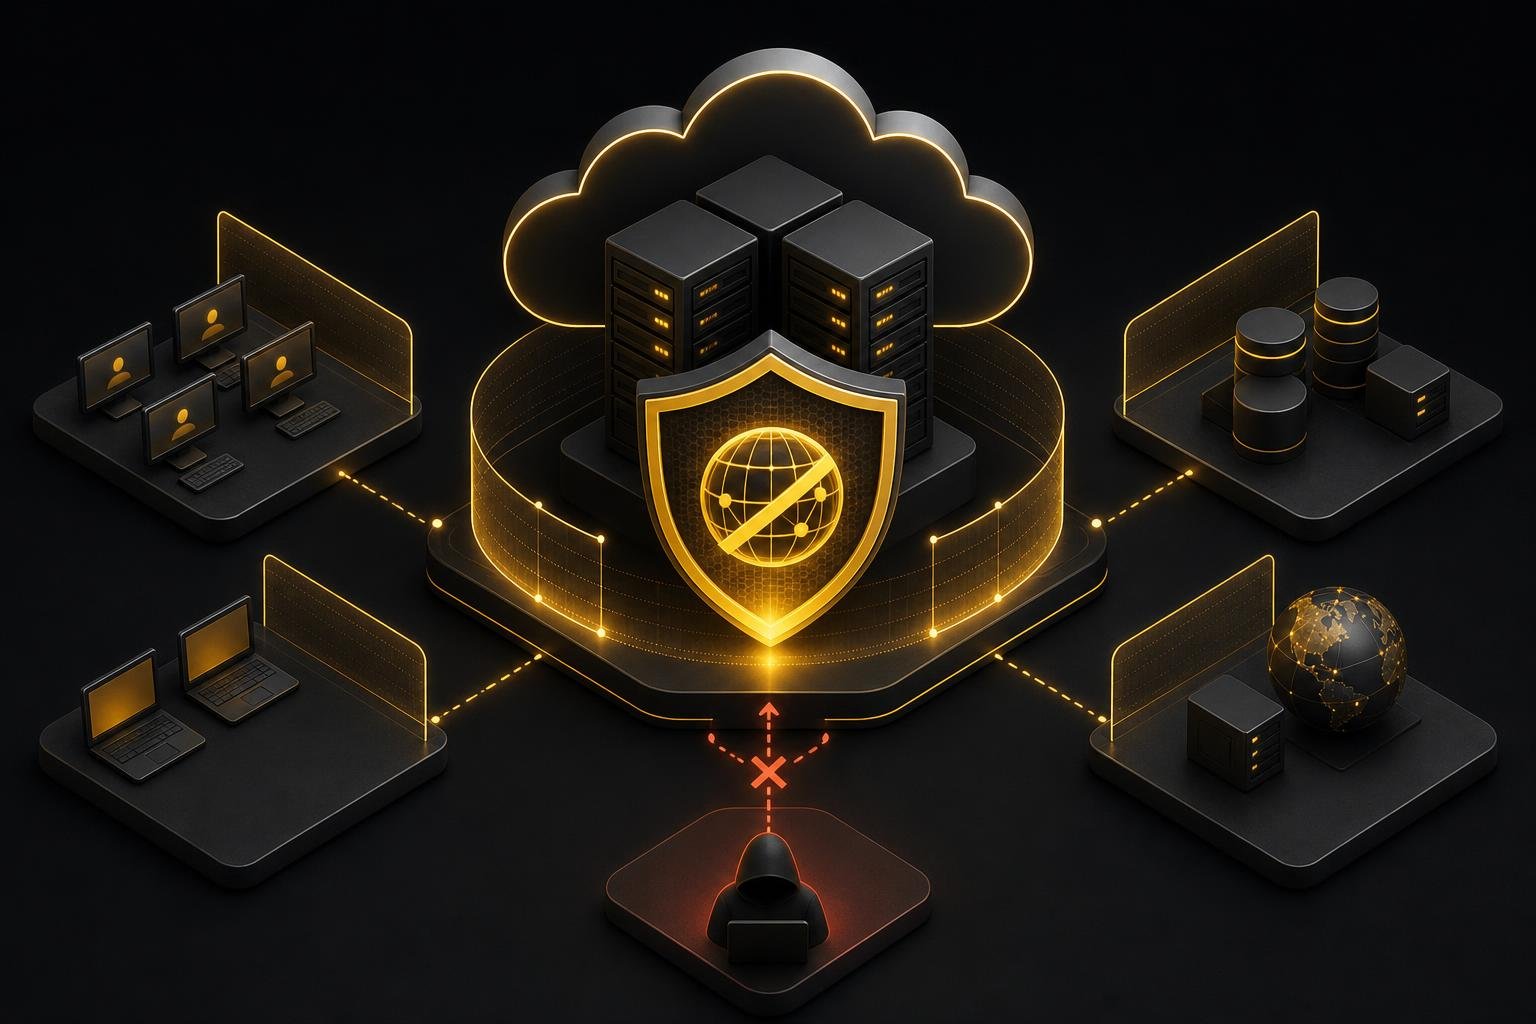
Implement network segmentation and firewalls to restrict backend services from accessing sensitive internal systems. This adds an extra layer of security, making it more difficult for an attacker to reach critical services even if they successfully exploit the SSRF vulnerability.
3. Whitelisting Outbound Requests
Use a whitelisting approach for outbound network requests made by your backend services. By allowing only specific IP addresses or domains to be accessed, you can reduce the Attack Surface. For instance, when fetching data from external APIs, only permit requests to known, trusted providers.
const allowedDomains = ['api.trustedprovider.com', 'another-trusted-domain.com'];

function isAllowedDomain(url) {
  const domain = new URL(url).hostname;
  return allowedDomains.includes(domain);
}

if (!isAllowedDomain(userRequestUrl)) {
  throw new Error('Domain not allowed');
}
4. Rate Limiting
Implement rate limiting on endpoints that handle external requests. Limiting the rate of requests helps prevent abuse, minimizing the chances of an SSRF attack succeeding by overwhelming the server with requests.
5. Regular Testing and Audit
Regularly conduct security audits and penetration testing to identify and fix potential vulnerabilities, including SSRF. Tools like OWASP ZAP can be utilized for automated scanning of vulnerabilities.
Common mistakes
- Neglecting input validation: Failing to properly validate user inputs can lead to SSRF vulnerabilities.
- Over-permissive configurations: Allowing too many outbound requests increases the risk of exploitation.
- Ignoring internal services: Often, developers focus only on external threats, overlooking potential internal exploit paths.
Frequently asked questions
What are common SSRF attack vectors?
Common SSRF attack vectors include sending requests to internal APIs, metadata services in cloud environments, or even accessing local services that the user is not supposed to reach.
Can SSRF vulnerabilities be mitigated with existing libraries?
Yes, existing libraries can help by providing built-in validation and whitelisting features, but they should be used as part of a broader security strategy rather than a complete solution.
How can I know if my application is vulnerable to SSRF?
Conduct penetration testing and security audits, or use automated tools to simulate SSRF attacks and identify potential weaknesses in your application.
What are the implications of an SSRF attack?
The implications can be severe, including unauthorized access to sensitive data, internal services, or sensitive instances in cloud environments, potentially leading to data breaches or service disruptions.
How often should I audit for SSRF vulnerabilities?
Regular auditing should be a part of your development lifecycle. Schedule audits at least quarterly or after significant changes in your application architecture.
Conclusion
Preventing SSRF vulnerabilities requires vigilance, best practices in input validation, network configurations, and constant monitoring. By incorporating these strategies into your development process, you can significantly reduce the risk of SSRF vulnerabilities in your backend services. For tailored solutions and expert advice, consider checking out our full-stack development services.